Source: https://mstdn.isometry.group/@Cahatstrophe2/117323121764942610
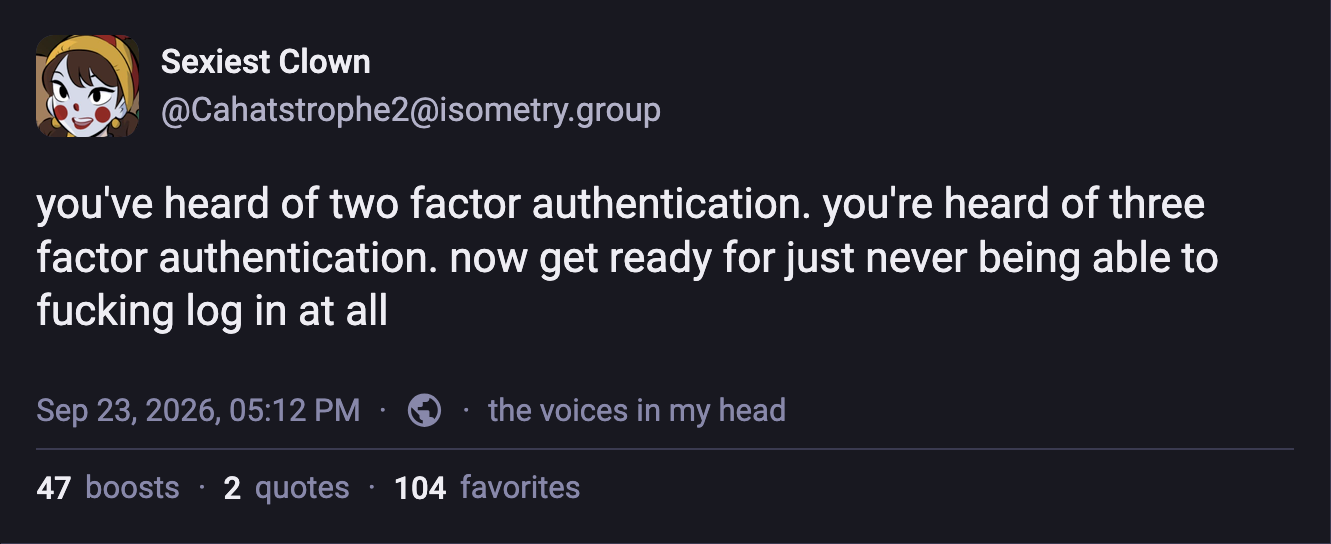
transcript
@Cahatstrophe2@isometry.group: you’ve heard of two factor authentication. you’re heard of three factor authentication. now get ready for just never being able to fucking log in at all
CMMC Level 2 has entered the chat.
I heard of passwordless login and I just can’t trust it
I kinda like the ones where you enter your email address and they email you a temporary password, that way we don’t have to ever remember or save a password. I think that’s secure enough, no?
I hate those magic links…
I am trying to login on a different device than I am able to receive and open the link on…Bloody impossible.
Now I either shorten the link somewhere or I chat me the name through discord or teams or whatever just so I can log my account in on a foreign machine.Hell no, then I have to find my phone to log into my email.
for text ones, but what about just email ones?
I still got to get my phone to 2FA into my email.
I especially love how it lets anyone that can access my email login in to any site that uses that pattern! That’s the best! So now someone only has to hack one thing to get access to all my stuff, it’s super convenient.
Don’t most websites use email when you press the “forgot password” button anyways?
Sites shouldn’t be letting you reset a password without answering security questions first either.
What was the middle name of your first highschool girlfriends dog?
I was stopped by a bouncer in a bar and was asked to show ID. I had forgotten my wallet with my ID, but luckily, I have the national app for the driver’s license. But to get that, I need to log in with my bank’s secure login. That login is behind 2FA so I needed to approve with a separate app and type in my password. My password is safely stored within a password manager. But that password manager’s access on my phone requires login through the microsoft single-sign-on. The microsoft login is buggy and requires me to manually log in through a separate URL.
I was arriving at the last step of my login before the bouncer announced that he saw that I was over the age limit of 18, so I didn’t have to continue. I was 33 at the time.
That’s why I hate banking apps. It’s 5-factor authentication for me and it’s seriously annoying.
The factors for logging into the internet banking are:
- Having a password manager - Something I have
- Remembering a master password - Something I know
- Having a banking app on the phone (🤮) - Something I have
- Using a password to log in to a user that has the app installed (I have a GrapheneOS and the banking app requires Gurgle services, so the services and apps must be separated) - Something I know
- Using a PIN inside the banking app to confirm the login - Something I know
Personally, im thrilled
I can’t stand how many websites are making me check my email or text messages for 2fa shit. Just let me use a TOTP, or even better, a passkey to get into my account!
Yes, it’s so slow and cumbersome. Fine as a backup but it also makes security worse if everyone uses email as then access to email gets everything.
Not good as a backup either because once they get in to your sms or email, they now have access to everything
Sounds pretty good actually
Every time I come up against that, I decide whatever I was trying to login for isn’t worth my time. It’s been happening a lot lately.
It’s like a monkey’s paw. I felt like I was spending too much time online a few years ago and slowly the internet has been giving me more reasons to not use it.
Same. Perhaps it’s by design. The internet used to be a lot more fun than it is now. Perhaps the people in charge of everything have been intentionally enshittifying the internet to break everyone’s addiction. But I thought they like it when we have addictions. The masses are easier to control when they’re hypnotized by things.
Twitch is the one that I don’t get. Their opaque password requirements feel like something you’d use to secure bioweapons.
Sites keep pushing Passkeys on me. I tried them. Did not work cross device. Did not integrate with every app. For now, I gave up on them.
It’s only a secure technology when it works and the key turns in the lock.
Yeah I don’t like those things. If your password is two or three words, with a special character and 3 numbers anywhere before between or after, it would take millions of years to brute force, and then you’re still covered with auth codes 2 factor. Theres no point in having a password so complex that you yourself can’t remember it.
The only exception is when a common password is found in a data breach, but you should have unique passwords for work and financial accounts and theres no guarantee that the password managers won’t be hacked at some point.
works cross-device with third party password managers (or smart keys like yubikeys)
Which defeats the point doesn’t it
Common misconception. The whole point of a password manager is so that you can have a unique password for every account. This means that of one site is compromised, only that one site is lost.
Passkeys take this a step further by taking a keylogger out of the equation since you’re no longer typing the password. And by using biometrics instead of a password to unlock your password manager, no password is ever typed significantly reducing the ability to steal it. Even better if it asks for both.
And to the point of one point of failure, this is always the case as you could get knocked on the head and forget all your passwords. You now only have to manage one potential point of security failure rather than however many accounts you have online.
Yubikey isn’t really biometrics though is it? You can like it with any body part or even a hot dog if you wanted.
At the end of the day, if someone is targeting you, specifically, they WILL succeed. See the Wrench Method. The point is making yourself a more difficult target for the blanket hits and data leaks.
This effort was using a third-party cross-platform password manager.
The specific case was a mobile game that needed to open a web browser that logged into a secondary account system, which I had set up to use passkeys. The in-app browser didn’t seem aware of my phone’s password manager plugin, and so it allowed no way to get in. Other times, logging in on a web browser with the password manager fully working simply gave an error - which could be blamed on the individual account provider, but then if I’m taking a chance on each passkey account, it’s again pointless.
Got I wanted a Yubikey for so long hearing about them. And earlier this year, Work got everyone Yubikeys for work, and they are essentially mandatory to use, and good fucking God so I hate Yubikeys.
Now I have this thing I have to carry around and dig out and plug in and my phone is going to eventually require it too and what the fuck happens when I inevitably lose it or it gets broken because it’s very flimsy feeling and already looks a little bent.
usually you have two of them with the same keys so you have a backup (at a safe place), but I do admit it feels really unsafe
I actually keep commenting that “I wish I could order more of these” especially because, as far as I can tell from what numbers I have seen, we paid almost nothing for these. I wanted to bulk order a dozen at the price they paid (if it’s accurate) and it would cost me less than one from Amazon.
Now you have to maintain two pieces of electronic to keep up-to-date.
Very grear.
That’s what Google use. I lost access to a Google account even though I had the right password because they randomly decided they didn’t think I was the account owner, and I didn’t have a phone number attached so the account recovery wasn’t available
Same thing happened with my Binance account. Then when I finally started to get some traction with customer service, my state banned Binance. And now it’s effectively gone forever
Same here. Any time I try to recover it they’re like “Nope, fuck you. Next time give us your phone number.”
I kept seeing a popup about adding a phone number because I might lose access to my account. I removed the phone number a decade ago. You mean my recovery email, OTP code, and backup codes can’t be used for recovery motherfucker!?!
Anyway I exported everything and closed my account because the fascists can eat a dick.
They may work, this was years ago before OTP was so widespread, and I don’t remember if it had a recovery email associated or not. I just remember I had the right password and it wouldn’t let me in anyway
Same thing happened to me. Recovery email means nothing to them, even with the correct username and password and recovery email code, I’m still locked out that account
Next is meta-factor authentication where part of the authentication process is making sure you perform each authentication method in the correct order as when you setup your account.
Then need to reset it when someone accidentally leaks the password to the unsecured database where everything was left in plain text.
I’ve been there, deleted my Gmail a while back and then two weeks later realized it was attached to a login I didn’t want to lose.
most sites when you use a vpn
meanwhile there are LLM call centers with no authentication
I called one, and the only authentication they asked was my birthday. instead of asking me my name or other details it just said “please confirm, are you [full name]?”
that’s all the security to access my private data!
then after going nowhere I managed to be transferred to a human and it took them a few minutes to authetify me.